
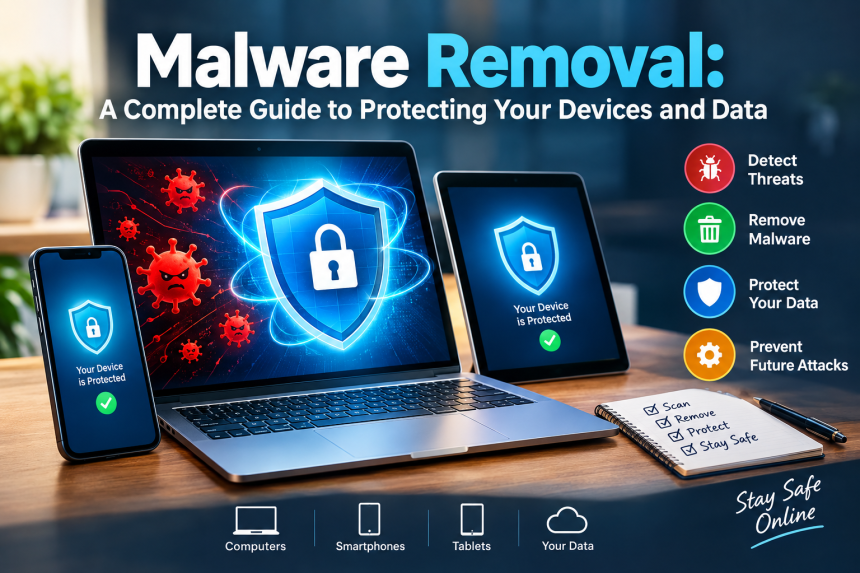
Malware can turn an ordinary day on your computer or phone into a stressful experience. Maybe strange advertisements suddenly appear, your browser redirects to unfamiliar websites, or your device becomes unusually slow. In some cases, malware quietly operates in the background without giving you any obvious warning.
The good news is that you can take practical steps to identify, remove, and prevent malicious software. You do not need to be a cybersecurity expert to understand the basics. Think of your device like your home: malware is an unwanted intruder, and the goal is to identify how it entered, remove it safely, and strengthen the doors and windows so it cannot easily return.
What Is Malware?
Malware is a broad term used for software designed to perform harmful, unwanted, or unauthorized activities on a device. The word comes from “malicious software,” and it can affect computers, smartphones, tablets, servers, and other connected systems.
Not every infected device behaves in the same way. Some threats are obvious, while others are deliberately designed to remain hidden. A malicious program might display unwanted advertisements, collect information, modify files, monitor activity, install additional programs, or provide unauthorized access to someone else.
Common forms of malware
Several types of malicious software are frequently encountered:
- Viruses: Programs that can attach themselves to files and spread when those files are opened or shared.
- Trojans: Harmful programs disguised as legitimate software or files.
- Spyware: Software designed to monitor activity or collect information without appropriate permission.
- Ransomware: A type of malicious software that locks or encrypts files and systems, preventing users from accessing their data until a ransom is demanded for its release.
- Adware: Software that displays excessive or unwanted advertisements.
- Worms: Programs capable of spreading between systems without requiring the same type of user interaction as traditional viruses.
- Keyloggers: Tools that can record keystrokes and potentially capture sensitive information.
- Rootkits: Malware designed to hide its presence and maintain unauthorized access.
These categories can overlap.A single infection can involve multiple malicious components, so deleting one suspicious file may not fully remove the threat or resolve the underlying issue.
How Malware Gets Onto a Device
Understanding how an infection happens is an important part of preventing another one. Malware usually does not magically appear. There is often an opportunity somewhere in the process.
One common route is a phishing message. You might receive an email, text message, or social media message containing a link or attachment that appears trustworthy. The message may create urgency by claiming that your account needs immediate attention.
Another route is downloading software from an unreliable source. Free programs, unofficial applications, pirated software, cracked programs, and suspicious browser extensions can sometimes contain unwanted components.
Malware can also take advantage of outdated operating systems, browsers, applications, or plugins. When security weaknesses remain unpatched, attackers may have opportunities to exploit them.
Other possible entry points include:
- Suspicious email attachments
- Fake software updates
- Malicious advertisements
- Compromised websites
- Unknown USB devices
- Untrusted browser extensions
- Pirated applications
- Fake technical-support messages
- Weak or reused account credentials
- Downloads from unofficial websites
This is why safe browsing habits matter. Your security software is an important layer of protection, but your everyday decisions are another major layer.
Warning Signs Your Device May Be Infected
Malware does not always announce itself. In fact, some malicious programs are specifically designed to operate quietly. However, certain changes may indicate that something deserves investigation.
A sudden decrease in performance is one possible warning sign. If a computer that normally works smoothly becomes unusually slow, repeatedly freezes, or uses excessive system resources, malware is one possibility among several.
Unexpected browser behavior can also be significant. You might notice that your homepage has changed, searches are redirected, unfamiliar extensions appear, or advertisements show up even when you are not visiting advertising-heavy websites.
Other warning signs include:
- Unknown applications appearing on the device
- Frequent crashes
- Unexpected pop-ups
- Security settings being changed without permission
- Unusual network activity
- Files being modified or becoming inaccessible
- Unfamiliar browser extensions
- Programs starting automatically
- Accounts showing suspicious activity
- Battery usage increasing unexpectedly on mobile devices
However, these symptoms do not automatically prove an infection. Hardware problems, outdated software, excessive background applications, browser issues, and storage limitations can produce similar effects.
The sensible approach is to investigate rather than immediately assume the worst.
What to Do First If You Suspect an Infection
If you believe malware may be present, avoid making the situation worse through rushed decisions.
First, consider disconnecting the affected device from the internet if there are signs of serious compromise, such as suspicious account activity, unusual network behavior, or ransomware-like behavior. Disconnecting can reduce opportunities for malicious software to communicate with external systems.
If the device contains important files, do not immediately connect unknown external drives or copy potentially infected files to another computer.
Protect important accounts
If you suspect that passwords may have been exposed, use a separate, trusted device to change important passwords. Prioritize email, financial, cloud-storage, and other accounts that could be used to reset additional credentials.
Enable multi-factor authentication wherever it is available. This adds another security layer because a stolen password alone may not be enough to access the account.
Avoid suspicious cleanup tools
One common mistake is searching for “instant malware removal” and downloading the first program that promises a perfect solution. Unfortunately, malicious websites sometimes imitate security software and use frightening warnings to persuade people to install more unwanted software.
Use security tools from reputable sources and avoid programs that rely on aggressive pop-ups, fake scans, or unrealistic promises.
How Malware Removal Usually Works
Removing malicious software is not as simple as deleting unfamiliar files or applications. Some legitimate system files and programs may have names or functions that seem unusual to the average user, so identifying malware requires careful evaluation rather than relying on appearance alone.
A safer process begins with an updated security solution. Update the operating system and security software when possible, then perform a full scan rather than relying only on a quick check.
A typical cleanup process
- Disconnect when appropriate: If there are strong signs of an active compromise, temporarily disconnect from the internet.
- Update security software: Make sure the security application has current threat information.
- Run a full scan: Allow the scanner to examine the device thoroughly.
- Review detected items: Check what the security tool identifies rather than deleting random files manually.
- Quarantine or remove threats: Follow the security software’s recommended process.
- Restart the device: Some cleanup actions require a reboot.
- Run another scan: A second examination can help confirm that the problem has been addressed.
- Update the operating system: Install available security updates.
- Review accounts: Look for suspicious logins, password changes, or other unusual activity.
- Restore carefully: If backups are needed, use clean and trustworthy copies.
Some threats are persistent and may interfere with ordinary security tools. In such cases, specialized offline or recovery scanning may be appropriate.
Removing Malware From a Windows Computer
Windows computers are common targets because they are widely used. Modern versions of Windows include built-in security features that can detect many types of threats.
Start by making sure Windows and its security components are updated. Then run a full security scan.
If normal scanning does not resolve the issue, a trusted offline scanning option may be useful. Offline scanning works in a different environment and can help identify threats that attempt to hide while the operating system is running.
Be careful with manual deletion
It may be tempting to search through system folders and delete suspicious files yourself. This can be dangerous. Removing a legitimate system component can create new problems or make the computer unstable.
Instead, use established security tools to identify and quarantine threats. If a problem continues after several scans, professional assistance may be safer than experimenting with unfamiliar commands or registry changes.
For serious infections involving financial information, business systems, or sensitive documents, consider obtaining professional help promptly.
Removing Malware From Mac Computers
Mac computers are not immune to malicious software. Although the threat landscape differs from Windows, attackers still target macOS users.
If your Mac starts showing unexpected pop-ups, unfamiliar applications, browser changes, unusual performance issues, or other suspicious behavior, investigate the cause.
Begin with system updates and review installed applications and browser extensions. Remove software you do not recognize only after confirming that it is not a legitimate component or application.
A reputable security application can provide additional scanning capabilities when needed.
Watch for fake security warnings
Mac users can encounter websites that display alarming messages claiming the computer is infected. These messages may be advertisements or attempts to persuade users to install questionable software.
A website cannot automatically perform a legitimate full security diagnosis simply because you opened a page. Be cautious when a webpage suddenly demands payment, a download, or immediate technical support.
Malware Removal on Smartphones and Tablets
Mobile devices deserve attention too. Android and iOS have built-in security mechanisms, but users can still encounter malicious links, fraudulent applications, phishing attempts, and account compromises.
On Android devices, review installed applications and permissions. Remove applications you do not recognize or no longer need, particularly if they request permissions unrelated to their purpose.
On iPhone and iPad, traditional malware behaves differently because of the platform’s security architecture, but users can still face phishing, fraudulent websites, malicious profiles, account theft, and other security problems.
Good mobile security habits include:
- Install applications through official app stores whenever possible.
- Keep the operating system updated.
- Review application permissions.
- Avoid suspicious links in messages.
- Use a strong device passcode.
- Enable multi-factor authentication on important accounts.
- Remove applications you no longer use.
- Avoid granting unnecessary permissions.
If suspicious behavior continues despite removing questionable applications and updating the device, backing up important data and performing a factory reset may sometimes be considered. Before doing so, make sure you understand what information will be erased and that essential data is backed up safely.
What About Files After an Infection?
One of the biggest concerns after an infection is personal data. Documents, photographs, work files, and other information may be valuable or irreplaceable.
If ransomware or another serious threat has affected your files, do not assume that paying money will guarantee recovery. Payment does not provide certainty that files will be restored or that attackers will not continue targeting you.
If you have a clean backup, recovery may be much easier. This highlights an important security principle: a backup is not merely a convenience; it can be a recovery lifeline.
A useful strategy is to maintain backups that are not continuously exposed to the same device. If malware can access every connected backup, an infection could potentially affect those copies as well.
Before restoring files, make sure the original infection has been addressed. Otherwise, you could reintroduce malicious software.
How to Prevent Future Infections
Prevention is usually easier than dealing with an infection after the damage has occurred.
Start with updates. Operating systems, browsers, applications, and security tools frequently receive fixes for security weaknesses. Delaying important updates for long periods can leave known vulnerabilities unaddressed.
Next, pay attention to downloads. Ask yourself: Do I really know where this file came from? If the answer is no, it is better to investigate before opening it.
Be particularly cautious with software that promises something unrealistic, such as unlimited premium features for free or immediate solutions to serious computer problems.
Build safer everyday habits
Use unique passwords for important accounts and consider a reputable password manager. Enable multi-factor authentication wherever practical.
Be skeptical of unexpected messages requesting passwords, payment details, verification codes, or urgent action. Even when a message appears to come from a familiar company, access the company’s official website or application directly instead of relying on the provided link.
Keep backups of important information. A backup strategy should include personal photographs, important documents, work files, and other data that would be difficult to replace.
Finally, learn to pause. Cybercriminals often rely on urgency. When a message tells you that you must act immediately, taking a few seconds to verify it can make a meaningful difference.
When Should You Ask a Professional for Help?
Many ordinary security problems can be addressed with built-in tools and careful steps. However, some situations deserve professional attention.
Consider getting expert assistance if the infection continues after repeated scans, security tools have been disabled, important files have been encrypted, financial information may have been exposed, or the device is connected to a business network.
Professional assistance is particularly important when the computer contains confidential business information or information belonging to other people.
Do not hide a serious security incident
If an infected device belongs to a workplace, school, organization, or shared environment, inform the appropriate administrator. Trying to quietly fix a serious incident can sometimes make investigation and recovery more difficult.
For financial accounts, contact the relevant financial institution through an official channel if you suspect unauthorized access. Monitor statements and account activity for unusual transactions.
Remember that security is not about achieving perfect protection. It is about reducing risk, detecting problems early, and having a sensible recovery plan.
Conclusion
Malware can be disruptive, but an infection does not mean that you have to panic. By recognizing warning signs, using trusted security tools, keeping software updated, protecting accounts, and maintaining reliable backups, you can significantly improve your digital safety.
Think of cybersecurity as maintaining your home. You would not leave every door unlocked and hope nothing happens. In the same way, a few consistent digital habits can create several layers of protection between you and malicious software.
The most valuable habit may be the simplest one: pause before you click, download, install, or share sensitive information.
Frequently Asked Questions
1. Can malware be removed completely?
Many malware infections can be detected and removed successfully with reputable security tools. However, the appropriate response depends on the type and severity of the infection. Serious compromises may require professional investigation, account recovery, or even a complete system reset.
2. Does a slow computer always mean malware is present?
No. Slow performance can have many causes, including insufficient storage, aging hardware, excessive startup programs, outdated software, or background processes. Malware is one possible explanation, but it should not be assumed without investigation.
3. Should I delete suspicious files manually?
Generally, no. A file that looks unfamiliar may still be a legitimate operating-system or application component. It is safer to use a reputable security tool to identify and quarantine potential threats rather than deleting system files manually.
4. Can a factory reset remove malware?
A factory reset can remove many forms of unwanted software by returning a device to a clean state, but the exact result depends on the threat and device. Before resetting, back up essential information carefully and make sure you understand what will be erased.
5. How can I reduce the chance of another infection?
Keep your operating system and applications updated, use reputable security software, download programs from trustworthy sources, avoid suspicious links and attachments, use strong unique passwords, enable multi-factor authentication, review application permissions, and maintain reliable backups. These habits create several layers of protection rather than relying on a single security measure.